MITRE ATT&CK Matrix
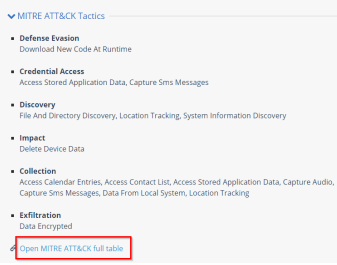
MITRE ATT&CK is a globally accessible knowledge base of adversary tactics and techniques based on real-world observations. When Mobile Security detects a malicious application, it uses the MITRE ATT&CK tactics and techniques to categorize and represent the risks and damages that this application may cause.
For more information about the MITRE ATT&CK Matrix, see https://attack.mitre.org/techniques/mobile/
Note:
The MITRE ATT&CK Matrix is available only if the application contains malware.
-
To view the complete MITRE ATT&CK Matrix for the application, click Open MITRE ATT&CK full table.
This matrix highlights the tactics and techniques used for the application.