
Events and Alerts
The Events & Alerts tab shows an audit trail of incidents and actions that occurred on the devices, for example, Application installation and Profiles detected on devices.
By default, the table displays all events for devices registered in your tenant. To view only the events that require remediation, click the Active events tab at the top.

| Item | Description |
|---|---|
| Date/Time |
Displays the date and time when the event occurred. |
| Severity level |
Note:
Low risk events do not trigger an alert on the end-user devices. |
| Attack Vector |
Specifies the nature of the Event/Alert:
|
| Threat Factors |
Specifies the threat factor for the event that occurred. Explains the reason for the severity level. |
| Event |
Specifies the user or the action taken by the Mobile Security solution.
|
| Event Details |
Additional details about the Event, such as name of application installed or removed Wi-Fi SSID or Identifying information, and so on. Event Details can link to an iOS Profile detail, Network detail, or App Analysis detail. |
| OS |
Operating System of the device (iOS/Android). It is determined by the information received from the device when the application is installed. |
| Policy |
Policy enforced on the device. |
| Device ID |
The device ID in the Mobile Security dashboard. |
| Device S/N |
Serial number of the device. |
| User email |
Device user's email address. It is manually set by the Admin or automatically by UEM when the devices are provisioned. |
For Android devices, you get a Phishing alert on the dashboard when Mobile Security detects and blocks a SMS phishing attempt on the mobile device. This feature works only if the end-user has granted access to Mobile Security Protect app to scan the SMS received on the device.
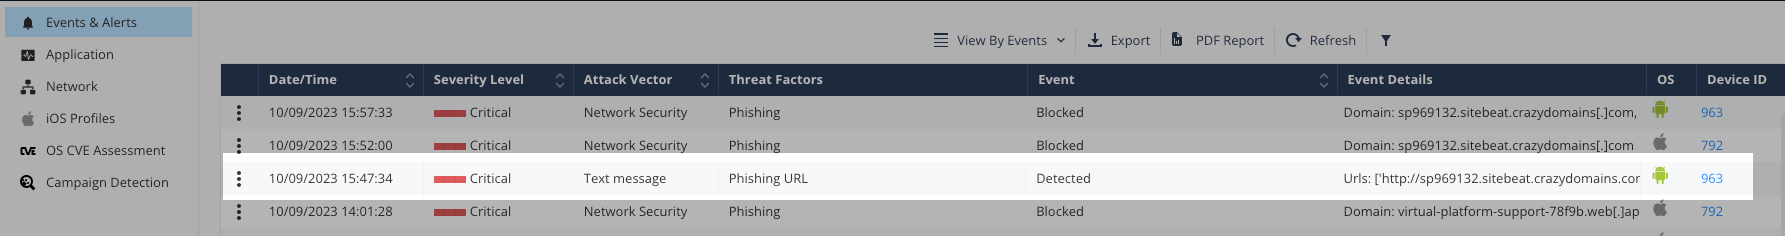
For more information on how to grant the access on the device:
-
For Android devices, see Preventing SMS Phishing in Android.
-
For iOS devices, see Preventing SMS Phishing in iOS.